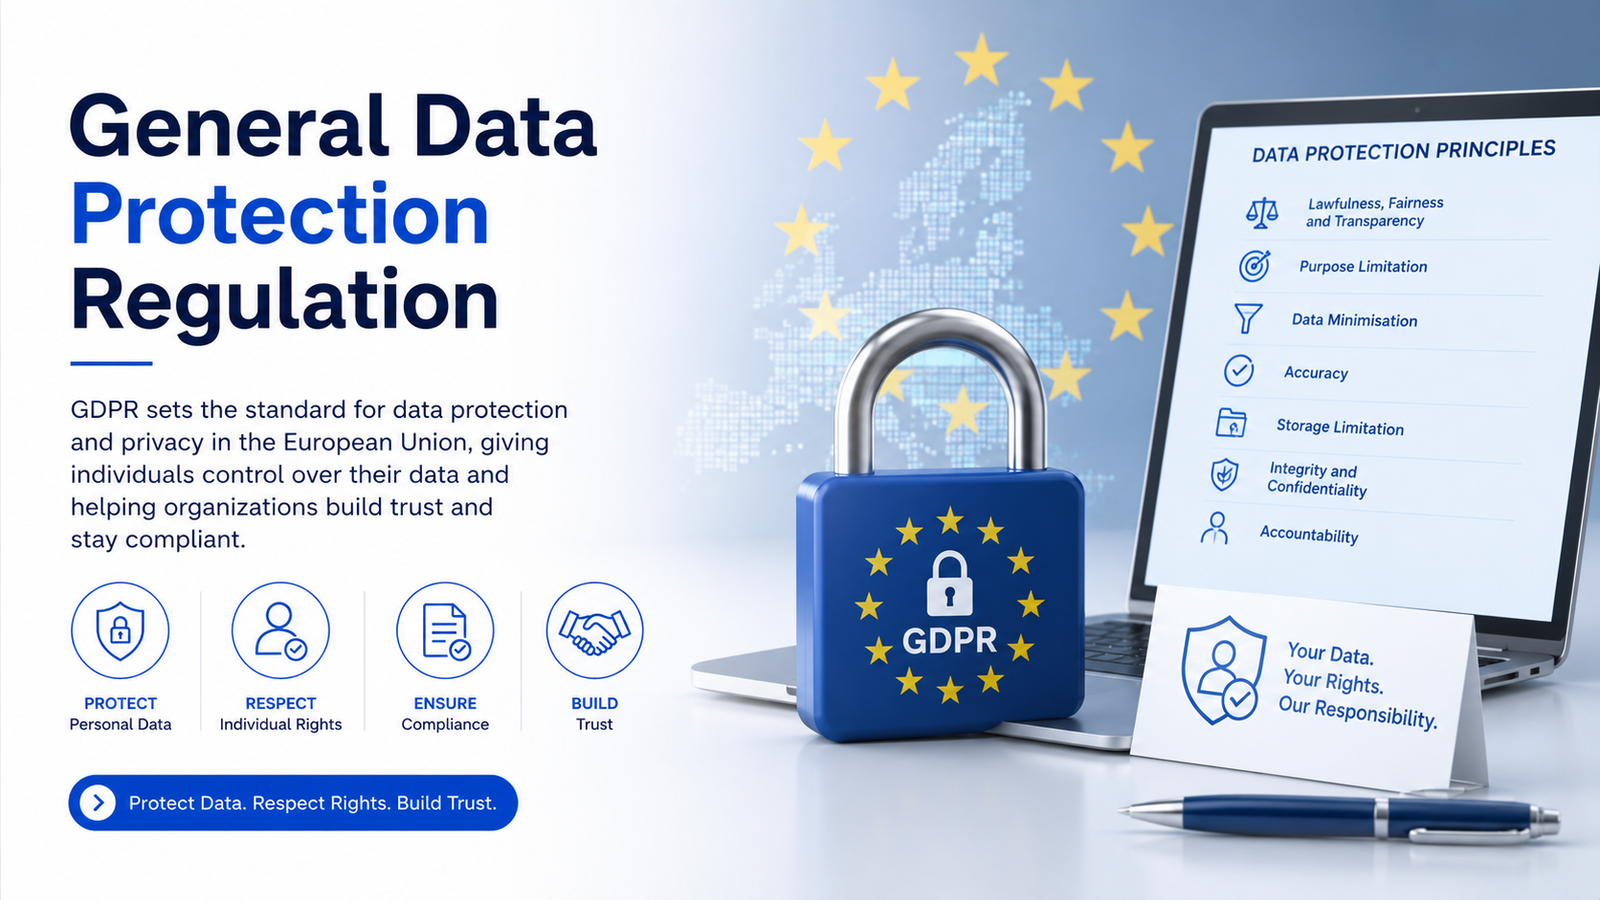
General Data Protection Regulation
The European Union General Data Protection Regulation (GDPR) is considered one of the strongest privacy and data protection laws in the world. It was introduced to modernise the earlier 1995 Data Protection Directive and officially came into effect on 25 May 2018. The GDPR establishes important rights for individuals regarding the protection and use of their personal data in the digital age. It also defines the responsibilities of organisations that collect or process personal information, sets requirements for compliance, and introduces strict penalties for violations of data protection rules.
When Do You Need GDPR Support
and What Are the Key Challenges?
Practical support for privacy compliance, data protection documentation, and GDPR readiness across digital and operational workflows.
-
Collecting EU citizens’ personal data
-
Using cookies or tracking on websites
-
Offering SaaS, apps, AI, or cloud services
-
Handling patient, customer, or employee data
-
Expanding into European markets
-
Collaborating with EU distributors or partners
-
Conducting EU email marketing or digital ads
-
Managing sensitive health or medical info
-
Addressing privacy concerns or audits
-
Preparing privacy policies and compliance documents
-
Divergent interpretations of GDPR rules across different EU member states' authorities
-
Lack of resources and expertise, especially for SMEs (e.g., appointing a DPO)
-
Inconsistent enforcement and widely varying fine levels between national DPAs
-
Consent fatigue and low user engagement with cookie/privacy notices
-
Complexity of cross-border data transfers (e.g., Transfer Impact Assessments after Schrems II)
-
Operational burden of documentation (e.g., Records of Processing Activities)
-
Limited DPA resources – insufficient staff and technical expertise to investigate and enforce effectively
Our Approach and What You Will Get
Practical GDPR support for businesses handling personal data, privacy obligations, documentation, and high-risk processing requirements.
-
Analyze business model and data flow
-
Assess GDPR applicability and identify gaps
-
Review privacy practices and documentation
-
Prepare GDPR-compliant documents
-
Support privacy measures implementation
-
Advise on consent, cookies, and data security
-
Assist with vendor and processor agreements
-
Support breach response readiness
-
Provide ongoing compliance guidance
-
Conduct Data Protection Impact Assessments (DPIAs) for high-risk processing
-
Designate a Data Protection Officer (DPO) where legally required
-
GDPR Applicability & Gap Analysis
-
Privacy & Cookie Policy Drafting/Review
-
Data Processing Agreements & Consent Management
-
Data Retention & Subject Rights Procedures
-
Data Breach Response SOP & Processing Records
-
Vendor Compliance Review & GDPR Roadmap
-
Employee Awareness & Technical/Organizational Measures
-
EU Representative Guidance (if applicable)
-
Data Protection Impact Assessment (DPIA)
-
Formal Data Protection Officer (DPO) Role
Why Choose Tacit Medtek and Case Example
Practical GDPR support for healthcare and digital businesses expanding into European markets.
-
Experienced regulatory and compliance professionals
-
Practical and implementation-focused approach
-
Customized GDPR solutions based on business type
-
Strong understanding of healthcare and medical data compliance
-
Support for startups, manufacturers, SaaS, AI, and healthcare sectors
-
Assistance with documentation, risk assessment, and compliance planning
-
Timely coordination and professional support
-
Focus on reducing compliance risks and improving data governance
-
Challenge: A digital healthcare company planning to expand into European markets was collecting patient and user information through its website and mobile application but lacked GDPR-compliant privacy practices and documentation.
-
Our Approach: Tacit conducted a GDPR applicability assessment, reviewed data collection processes, prepared GDPR-compliant privacy and cookie policies, advised on consent mechanisms, and supported implementation of data protection procedures and vendor agreements.
-
Outcome: The company improved its data privacy framework, strengthened customer trust, reduced compliance risks, and became better prepared for partnerships and operations involving EU users and stakeholders.
FAQ
Frequently Asked Questions
To help governments, businesses, data protection authorities, and citizens prepare for GDPR implementation on 25 May 2018. Although adopted in 2016, additional steps like updating national laws and establishing the European Data Protection Board was needed.
- Assisted EU Member States and data protection authorities
- Supported the creation of the European Data Protection Board
- Organised discussions with businesses and SMEs
- Launched online compliance tools
- Funded training programs and awareness initiatives
- Greater individual control over personal data
- Stronger enforcement of data protection laws
- Simplified international data transfers
- Establishment of stronger global data protection standards
- Organisations established in the EU processing personal data
- Organisations outside the EU offering goods/services to, or monitoring behaviour of, individuals in the EU
Enquire Now
Fill in the form and our team will get back to you shortly.
Reach our regulatory experts directly.