500+ Clients
20+ Years Experience
CDSCO Experts
Pan India Support
ISO Certification

Quick Snapshot

  • Service: ISO 27001 Consultancy & Implementation Support
  • Who Can Apply:
    • SaaS Companies
    • IT & Software Organizations
    • Healthcare Platforms
    • Medical Device Startup Companies
    • Cloud Service Providers
    • Technology Organizations
    • Businesses handling sensitive information
  • Timeline: The ISO 27001 implementation timeline depends on the organization size, ISMS scope, existing documentation, business processes, and overall implementation readiness.
  • Fee: Consultancy fees are calculated after understanding the project scope, operational structure, multi-location requirements, technical environment, and certification readiness level.

What is ISO 27001?

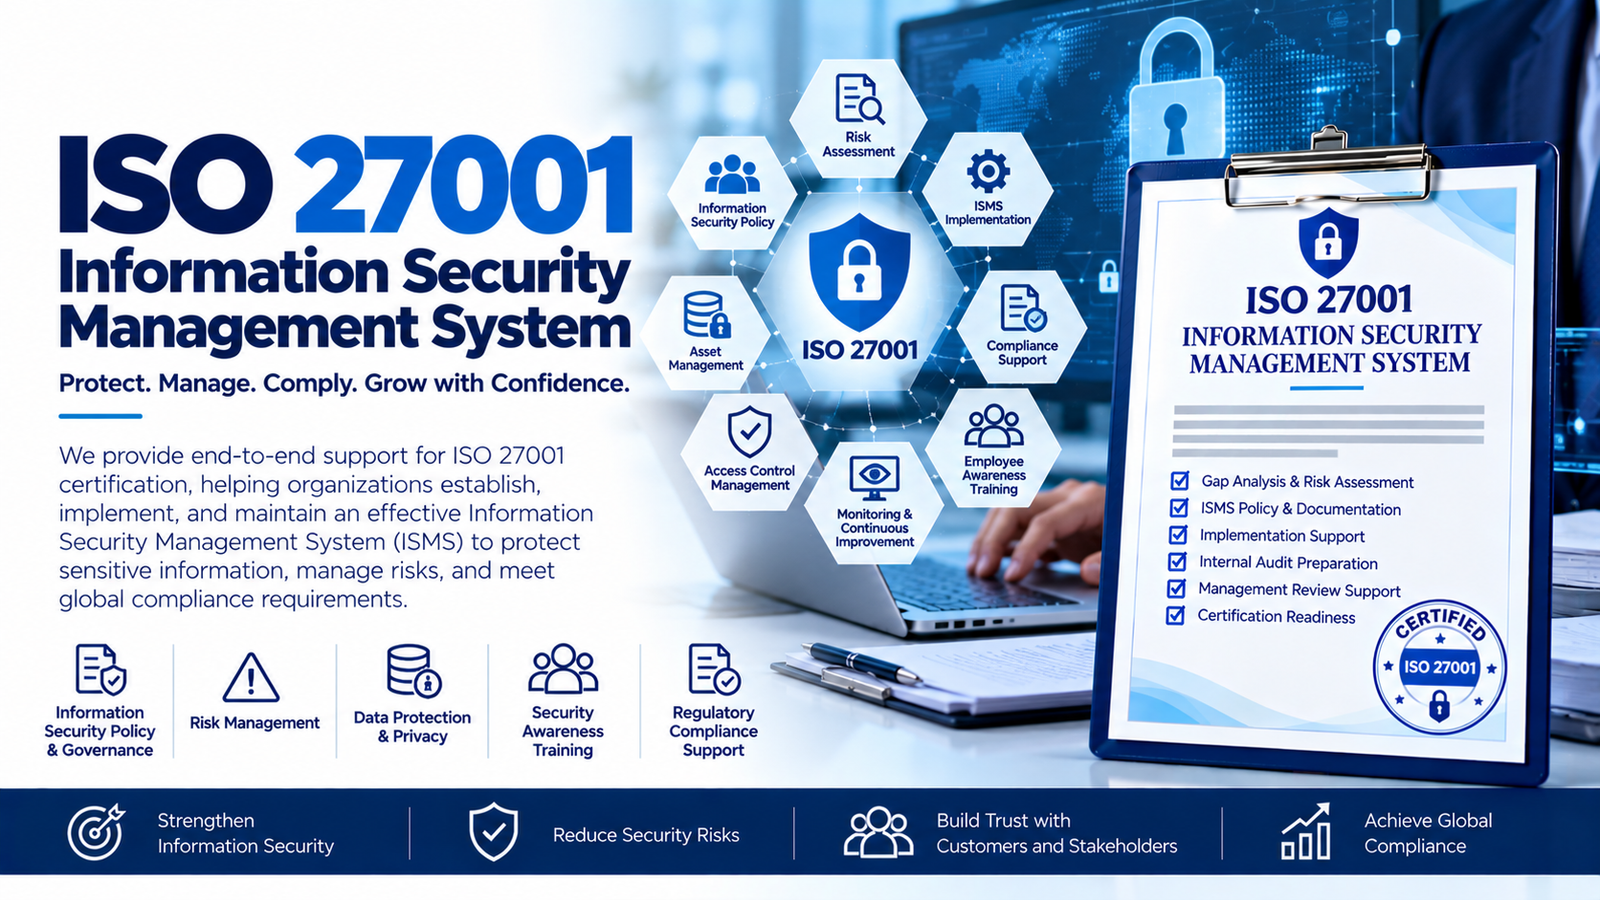
ISO/IEC 27001 is the internationally recognized standard for Information Security Management Systems (ISMS). It helps organizations identify, manage, and reduce information security risks in a structured and systematic way.

In today’s digital world, companies handle important customer and business information every day. Without proper security systems, businesses may face data breaches, cyber risks, and loss of customer trust.

ISO 27001 helps organizations build a strong security framework by implementing policies, controls, risk management practices, and continuous monitoring processes.

It also demonstrates to clients, partners, and regulators that your organization takes information security seriously.

When Do You Need ISO 27001?

ISO 27001 support helps organizations establish structured information security processes, reduce cyber risks, meet customer expectations, and strengthen trust.

When Do You Need ISO 27001?
  • When your organization handles sensitive customer or business data
  • When clients request information security compliance certification
  • When working with healthcare, SaaS, IT, fintech, cloud, or software services
  • When you want to improve cybersecurity governance
  • When preparing for enterprise or international clients
  • When you want to reduce security risks and incidents
  • When your organization is scaling and needs structured security processes
  • When you want to strengthen customer trust and business credibility
  • When you need compliance support for regulatory or contractual requirements

ISO 27001 is especially valuable for startups, software companies, cloud service providers, medical device companies, healthcare platforms, and organizations handling confidential information.

Key Challenges Organizations Face
  • Lack of structured information security processes
  • Difficulty identifying security risks
  • Missing or incomplete security documentation
  • Weak access controls and asset management
  • No formal incident response process
  • Employee awareness and training gaps
  • Vendor and cloud security concerns
  • Audit preparation challenges
  • Difficulty understanding ISO requirements
  • Limited internal resources or expertise

Without proper guidance, organizations may create unnecessary documentation or overlook critical compliance requirements.

Our Approach and What You Will Get

Practical, business-focused support for building a manageable, realistic, and audit-ready Information Security Management System (ISMS).

Our Approach
  • Gap Assessment: Review of current processes, systems, and documentation to identify compliance gaps.
  • Scope Definition: Define the ISMS scope based on business operations, locations, applications, teams, and infrastructure.
  • Risk Assessment & Risk Treatment: Identify information security risks and implement suitable controls aligned with ISO 27001 Annex A requirements.
  • Documentation Support: Prepare and customize required policies, SOPs, templates, registers, and records according to organizational activities.
  • Control Implementation Guidance: Support practical controls such as access control, backup management, incident response, supplier security, and secure operations.
  • Employee Awareness & Training: Conduct awareness sessions covering security responsibilities and compliance expectations.
  • Internal Audit & Management Review: Assist with internal audits and management review meetings before certification audits.
  • Certification Audit Support: Provide support during Stage 1 and Stage 2 certification audits.

Our focus is on building a manageable, realistic, and audit-ready ISMS instead of unnecessary paperwork.

What You Will Get (Deliverables)
  • ISO 27001 implementation roadmap
  • ISMS scope definition support
  • Gap analysis and compliance guidance
  • Risk assessment and risk treatment support
  • Information Security Policy documentation
  • Access Control Policy
  • Backup & Recovery Procedure
  • Incident Management Procedure
  • Asset Inventory Register
  • Risk Register preparation
  • Supplier and Vendor Evaluation Templates
  • Document control support
  • Employee awareness and training guidance
  • Internal audit readiness support
  • Certification audit preparation and assistance during Stage 1 and Stage 2 audits
  • End-to-end audit support

All documents and templates are customized according to your business activities, operational processes, risk level, and compliance requirements.

Why Choose Tacit Medtek and Case Example

Practical, business-friendly ISO 27001 implementation support focused on effective controls, audit readiness, and long-term compliance.

Why Choose Tacit Medtek

Organizations choose Tacit Medtek because we focus on practical implementation rather than documentation alone.

  • Industry-focused compliance expertise
  • Practical and simplified implementation approach
  • Customized documentation support
  • Strong understanding of healthcare, medical device, SaaS, and technology environments
  • End-to-end audit support
  • Business-friendly compliance processes
  • Faster implementation guidance
  • Support for integrated management systems
  • Long-term compliance support

We work closely with your team to make ISO implementation understandable, manageable, and effective.

Case Example
  • Challenge: A growing healthcare technology company handling sensitive patient information needed ISO 27001 certification to meet client security requirements and strengthen internal security controls.
  • Key Issues: Incomplete security documentation, lack of formal risk management, limited access-control processes, no structured incident-response mechanism, and audit-readiness concerns.
  • Our Approach: Conducted a complete gap analysis and developed a structured implementation plan covering ISMS scope definition, risk assessment and treatment, security policy development, access-management improvements, backup and incident-management procedures, employee awareness sessions, and internal audit and management review preparation.
  • Outcome: The organization successfully established an ISO 27001-compliant ISMS and completed certification readiness within the planned timeline.

Key Improvements: Better security governance, improved access control, increased client confidence, structured risk management, improved audit preparedness, and a stronger information security culture.

FAQ

Frequently Asked Questions

01
What is ISO 27001?

ISO 27001 is an international standard for establishing and maintaining an Information Security Management System (ISMS).

02
Who should implement ISO 27001?

Any organization handling sensitive information can implement ISO 27001, including IT companies, SaaS providers, healthcare organizations, startups, and cloud-based businesses.

03
How long does ISO 27001 implementation take?

Implementation timelines depend on organization size, scope, and existing processes. Typically, implementation may take a few weeks to several months.

04
Is ISO 27001 mandatory?

ISO 27001 is generally voluntary, but many clients, regulators, and contracts require organizations to demonstrate strong information security practices.

05
What is SoA in ISO 27001?

Statement of Applicability (SoA) is a document that defines which Annex A security controls are applicable to the organization and why.

06
Does ISO 27001 require risk assessment?

Yes. Risk assessment and risk treatment are core requirements of ISO 27001.

07
Can startups implement ISO 27001?

Yes. Startups can implement ISO 27001 to improve security maturity and build client trust.

Enquire Now

Send Enquiry

Fill in the form and our team will get back to you shortly.

Your information is secure and will never be shared.

Send Message