500+ Clients
20+ Years Experience
CDSCO Experts
Pan India Support
ISO Certification

Quick Snapshot

  • Standard: ISO 27701
  • Focus: Privacy Information Management System (PIMS)
  • Applicable To: Organizations processing Personally Identifiable Information (PII)
  • Timeline: Depends on organization size and implementation readiness
  • Deliverables:
    • Gap Assessment
    • PII Mapping
    • Privacy Risk Assessment
    • PIMS Documentation
    • Internal Audit Support
    • Certification Readiness
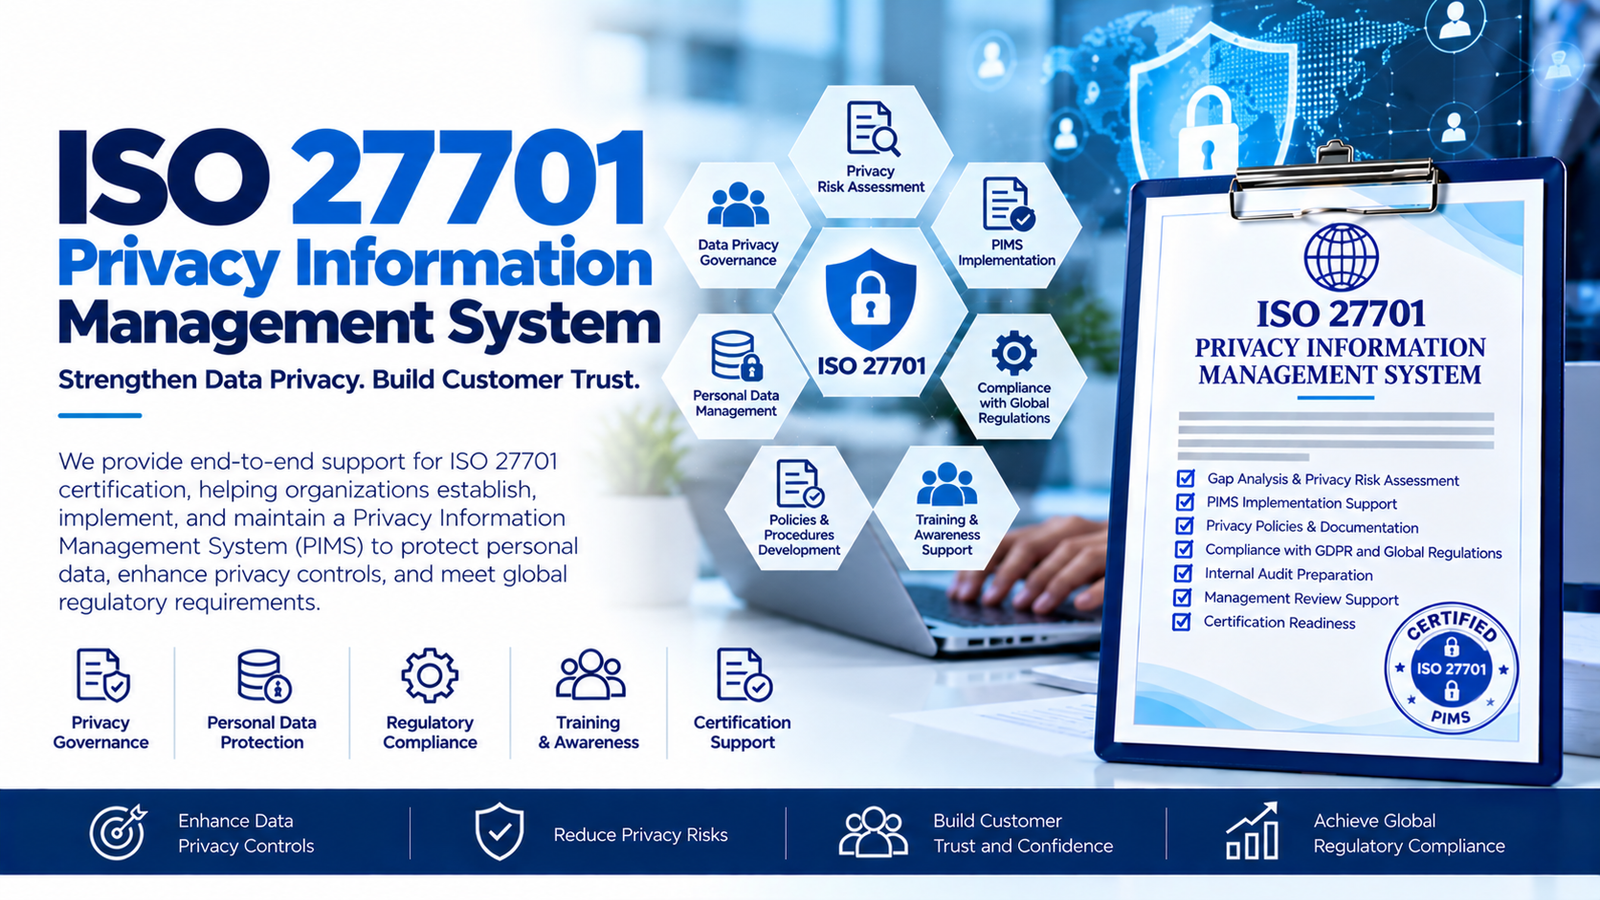
  • Purpose: Establish, implement, maintain, and continually improve a Privacy Information Management System (PIMS) to manage Personally Identifiable Information (PII).

What is ISO 27701?

An international standard for privacy information management, ISO/IEC 27701 builds upon ISO/IEC 27001 to assist organisations in creating, implementing, maintaining, and continuously enhancing a Privacy Information Management System (PIMS).

It offers a methodical framework for handling Personally Identifiable Information (PII), bolstering data privacy governance, and proving accountability to stakeholders, partners, customers, and authorities.

Organisations might benefit from ISO 27701 certification as privacy laws continue to change globally.

  • Systematically safeguard sensitive and personal information
  • Show that you are prepared to comply with privacy regulations.
  • Increase stakeholder and customer trust
  • Minimize privacy risks and incidents
  • Boost operational transparency and governance
  • Encourage safe digital transformation projects

ISO 27701 is becoming more and more of a competitive and legal requirement for businesses that handle customer, employee, patient, or partner data.

When Do You Need ISO 27701 Certification?

ISO 27701 support helps organizations strengthen privacy governance, manage personal data responsibly, and extend an existing ISO 27001-based information security framework.

When Do You Need ISO 27701?
  • When your company processes or stores personal data (PII)
  • When operating in regulated sectors such as healthcare, fintech, SaaS, e-commerce, telecom, or insurance
  • When working with international clients requiring privacy assurance
  • When stronger privacy governance and accountability are needed
  • When you already maintain ISO 27001 and want to extend it to privacy management
  • When facing increasing customer or regulatory scrutiny around data privacy
  • When aligning with global privacy expectations and best practices
Key Challenges
  • Unclear privacy governance structures
  • Difficulty identifying and classifying PII
  • Gaps between security controls and privacy obligations
  • Managing third-party privacy risks
  • Demonstrating compliance evidence during audits
  • Lack of documented privacy processes
  • Balancing operational efficiency with privacy requirements
  • Integrating privacy into existing business workflows

Our Approach and What You Will Get

Practical, business-aligned support for implementing a Privacy Information Management System (PIMS) and preparing for ISO 27701 certification.

Our Approach
  • Privacy Readiness Assessment
  • PII Mapping and Risk Assessment
  • Policy and Documentation Development
  • Control Implementation Support
  • Awareness and Training
  • Internal Audit and Certification Readiness
  • Certification Support
What You Will Get (Deliverables)
  • Gap Assessment Report
  • Privacy Risk Assessment
  • PII Inventory and Data Flow Mapping
  • Privacy Policies and Procedures
  • PIMS Documentation Support
  • Risk Treatment Plan
  • Internal Audit Support
  • Management Review Guidance
  • Employee Awareness Materials
  • Audit Readiness Support
  • Certification Coordination Assistance

Why Choose Tacit Medtek and Case Example

Practical, industry-focused support for privacy governance, ISO 27701 implementation, audit readiness, and long-term compliance.

Why Choose Tacit Medtek
  • Experienced compliance professionals
  • Simple and practical approach
  • End-to-end implementation support
  • Industry-focused expertise
  • Faster and smoother certification process
  • Customized solutions for your business
Case Example
  • Client Profile: A fast-growing digital healthcare platform handling sensitive patient data required stronger privacy controls and compliance support to meet enterprise client requirements.
  • Challenge: Limited formal privacy governance, inconsistent PII-handling practices, vendor privacy-management gaps, and a lack of audit-ready documentation.
  • Our Approach: Conducted a privacy gap assessment, implemented ISO 27701-aligned controls, developed required documentation, and supported audit-readiness activities.
  • Outcome: Improved privacy governance maturity, better visibility into personal-data processing, enhanced customer trust, stronger audit preparedness, and successful alignment with international privacy best practices.

FAQ

Frequently Asked Questions

01
How long does certification take?

The certification timeline depends on your organisation's size, the maturity of its existing management systems, and the level of implementation required.

02
Why should we obtain ISO 27701 certification?

Certification demonstrates your commitment to data privacy to stakeholders, clients, and regulatory agencies. It combines your security and privacy governance, gives you a competitive edge in vendor evaluations, and aids in the development of digital trust.

03
Who issues the certification and does the audit?

Accredited, impartial certification agencies grant certification. The audit is conducted in phases, starting with a preliminary examination of your paperwork (Stage 1) and concluding with a comprehensive on-site or virtual assessment of the practical operation of your PIMS (Stage 2).

Enquire Now

Send Enquiry

Fill in the form and our team will get back to you shortly.

Your information is secure and will never be shared.

Send Message