500+ Clients
20+ Years Experience
CDSCO Experts
Pan India Support
INFORMATION SECURITY & PRIVACY

Quick Snapshot

  • Who Can Apply?IT Companies, SaaS Providers, Cloud Service Providers, Data Centres, AI/ML Companies, Fintech Startups, Healthcare IT, and any organization handling customer data.
  • TimelineTypically 3–6 months depending on organization size, system complexity, existing security maturity, and SOC 2 scope.
  • ServiceSOC 2 Compliance Consultancy & Implementation Support

What is SOC 2 Compliance (System & Organization Controls)?

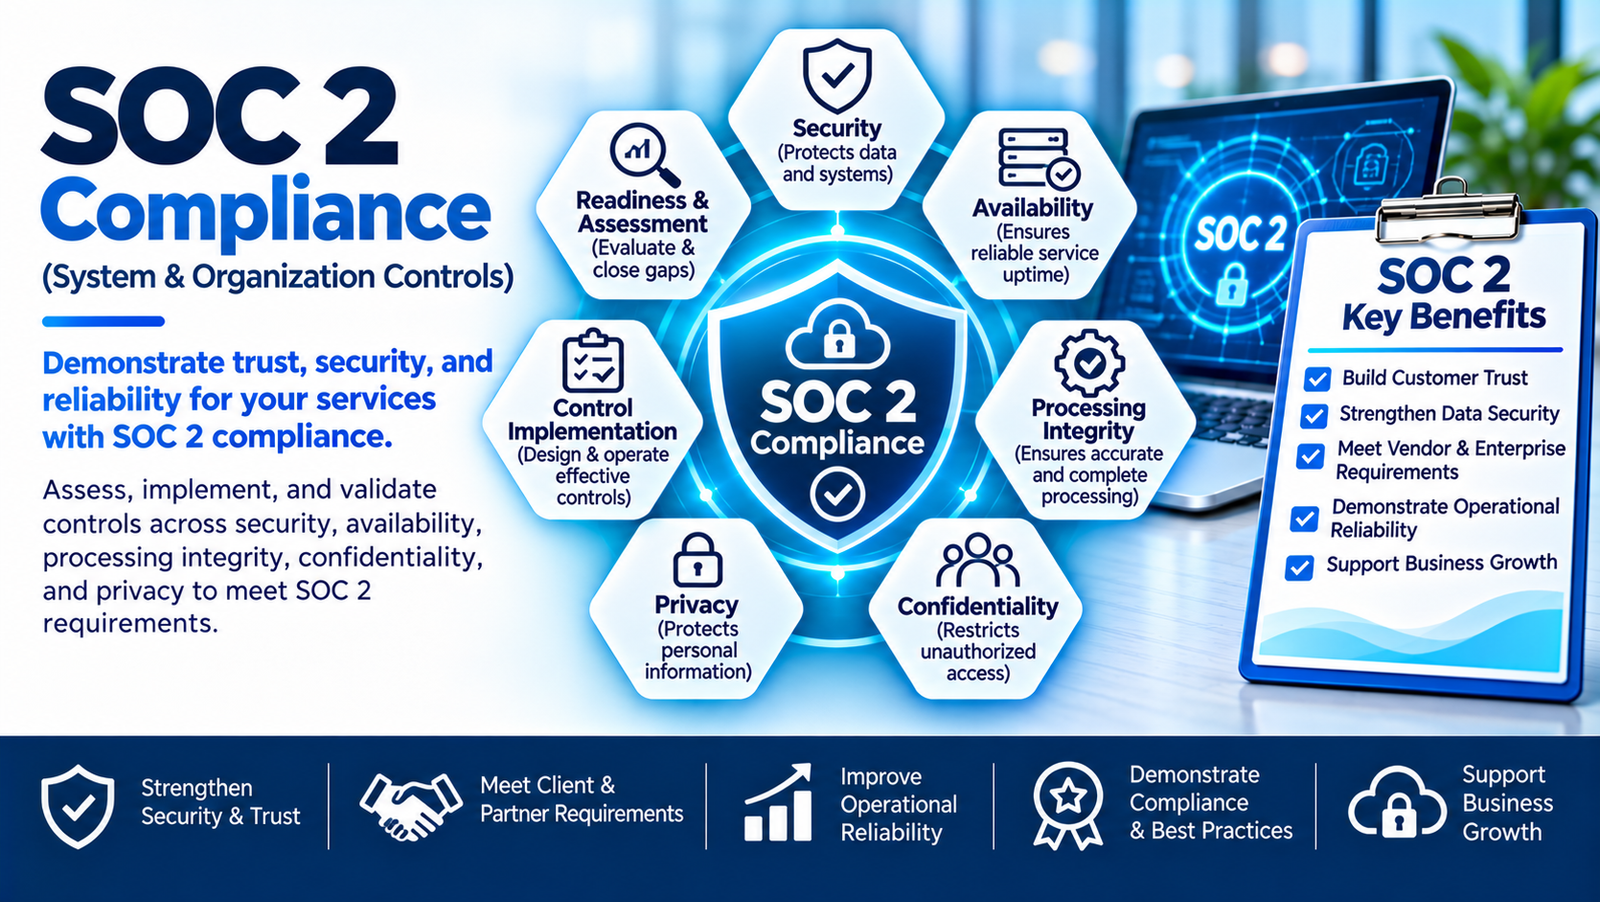
SOC 2 Compliance is a cybersecurity and data protection standard developed by the American Institute of Certified Public Accountants for companies that handle customer data. It helps organizations demonstrate that they have proper security controls to protect sensitive information, maintain data privacy, and manage cybersecurity risks. SOC 2 is commonly used by SaaS, IT, cloud, and technology companies.

When Do You Need SOC 2 Compliance Support?

Practical support for SaaS, cloud, and IT service organizations preparing for SOC 2, strengthening security controls, and building customer trust through structured compliance readiness.

When Do You Need SOC 2 Compliance Support?
  • When handling customer or sensitive business data
  • When providing SaaS, cloud, or IT services
  • When clients request cybersecurity compliance proof
  • When working with international customers or enterprises
  • When improving data security and privacy practices
  • When preparing for business growth, partnerships, or investments
  • When building customer trust and market credibility
Key Challenges
  • Understanding SOC 2 requirements and applicability
  • Identifying gaps in existing security controls
  • Preparing required policies and documentation
  • Managing cybersecurity and data privacy risks
  • Implementing access control and monitoring systems
  • Maintaining audit readiness and compliance evidence
  • Managing vendor and third-party security controls
  • Ensuring continuous compliance and system monitoring

Our Approach and What You Will Get

End-to-end SOC 2 readiness support, from gap assessment and policy development to audit preparation and continuous compliance maintenance.

Our Approach
  • Assess your organization’s SOC 2 readiness and compliance scope
  • Identify gaps in security controls, policies, and processes
  • Develop required SOPs, policies, and compliance documentation
  • Support implementation of security and risk-management controls
  • Assist with evidence collection and audit preparation
  • Provide guidance for continuous monitoring and compliance maintenance
  • Help align your organization with SOC 2 security best practices
What You Will Get (Deliverables)
  • SOC 2 Readiness Assessment Report
  • Gap Analysis and Remediation Plan
  • Security Policies and Procedures (Access Control, Incident Response, Change Management, etc.)
  • SOC 2 Scope Definition Document
  • Risk Assessment and Risk Management Documentation
  • Vendor and Third-Party Security Assessment Records
  • Evidence Collection Templates and Audit Checklists
  • Business Continuity and Disaster Recovery Plan
  • Employee Security Awareness Training Materials
  • Corrective and Preventive Action (CAPA) Support
  • Internal Audit Support Documentation
  • Security governance review documentation
  • SOC 2 Type I / Type II Audit Preparation Support

Why Choose Tacit Medtek and Case Example

Practical, end-to-end SOC 2 readiness support for healthcare IT, SaaS, and medical device software companies seeking to strengthen security, meet enterprise requirements, and support business growth.

Why Choose Tacit Medtek?
  • Practical SOC 2 readiness support tailored for healthcare IT, SaaS, and medical device software companies
  • Deep understanding of data security requirements at the intersection of SOC 2, HIPAA, and GDPR
  • Structured gap-assessment-first methodology to identify the fastest path to SOC 2 compliance
  • End-to-end support from scope definition through Type I and Type II audit preparation
  • Experience supporting startups and SMEs with cost-effective, right-sized compliance programs
  • Dedicated team providing fast response and hands-on implementation guidance throughout the engagement
Case Example
  • Challenge: A healthcare SaaS company providing a cloud-based patient data management platform was repeatedly asked by enterprise hospital clients to provide SOC 2 compliance proof. Without it, they were losing contracts. They had no existing security documentation or compliance program in place.
  • Our Approach: Conducted a SOC 2 readiness assessment and defined compliance scope; identified critical gaps in access control, incident response, and data encryption practices; developed security policies, SOPs, and an evidence-collection framework; implemented risk-management and vendor-assessment processes; supported internal audit activities and audit-evidence preparation; and prepared the organization for a SOC 2 Type I audit.
  • Outcome: The company achieved SOC 2 Type I compliance within a few months, successfully meeting enterprise client requirements and closing previously stalled contracts.

FAQ

Frequently Asked Questions

01
What is the difference between SOC 2 Type I and Type II?

SOC 2 Type I assesses whether security controls are properly designed at a single point in time. SOC 2 Type II evaluates whether those controls operated effectively over a defined period, typically 6 to 12 months. Most enterprise clients require Type II.

02
Can you help with documentation and SOPs?

Yes. We support SOC 2 documentation including security policies, procedures, risk assessments, access control documentation, incident response procedures, vendor management records, and audit evidence preparation.

03
Do you assist with audits and certification preparation?

Yes, we help companies prepare for audits by identifying gaps, improving compliance systems, supporting internal audit activities, and ensuring documentation is aligned with regulatory expectations.

04
Do you work with startups or early-stage companies?

Yes, we regularly support startups and new manufacturers by simplifying regulatory requirements, building compliant systems from the ground up, and guiding them step-by-step until they are ready for approval or certification.

Enquire Now

Send Enquiry

Fill in the form and our team will get back to you shortly.

Your information is secure and will never be shared.

Send Message